Telecom Department Advisory on IMEI Tampering and Security
Source:PIB ↗
কেন এটি গুরুত্বপূর্ণ
It underscores critical government initiatives regarding telecom security and consumer protection against device counterfeiting and cybercrimes under evolving legal frameworks like the Telecommunications Act.
সারসংক্ষেপ
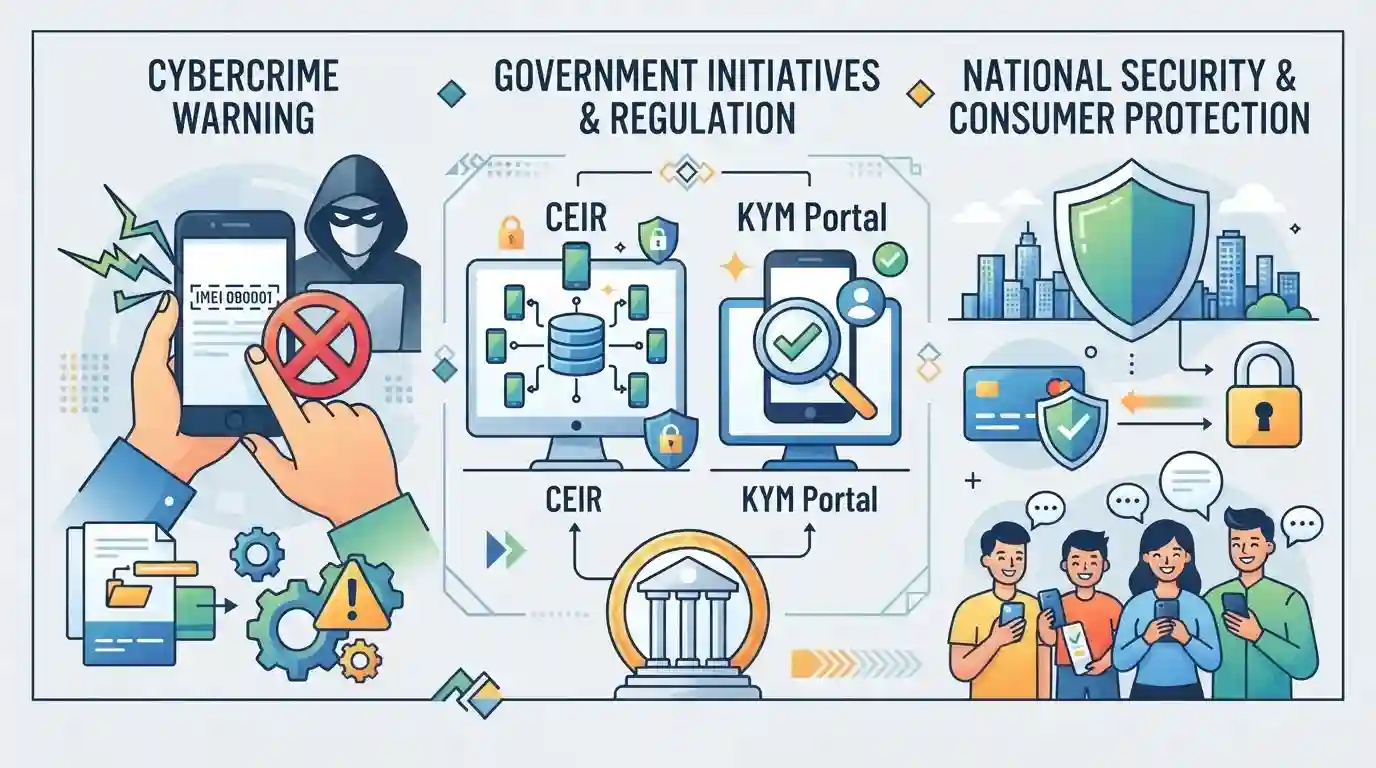
The Department of Telecommunications (DoT) issued a public advisory warning citizens against IMEI tampering and the misuse of telecom identifiers, emphasizing that altering device identities is a severe cybercrime. The government highlighted digital tools like the Central Equipment Identity Register (CEIR) and Know Your Mobile (KYM) portal to safeguard users, prevent financial frauds, and enhance national security.
মূল বিষয়
- The Department of Telecommunications (DoT) has issued a public advisory cautioning citizens against IMEI tampering and the misuse of telecommunication identifiers.
- Tampering with International Mobile Equipment Identity (IMEI) numbers is a serious cyber offense under Indian law, enabling the cloning of devices used in illegal and anti-national activities.
- The advisory highlights mechanisms like the Central Equipment Identity Register (CEIR) and the 'KYM - Know Your Mobile' app/portal to verify device authenticity and block stolen or lost phones.
- Such measures are crucial for protecting consumer security, preventing financial fraud, and strengthening national cybersecurity infrastructure.
গুরুত্বপূর্ণ শব্দ
The Telecommunications Act 2023

A key legislation governing India's telecom sector, which penalizes the tampering of telecom identifiers like IMEI numbers with imprisonment up to 3 years and fines up to ₹50 lakh.
UPSC context
Important for GS Paper II/III (Governance, Internal Security, and Telecom Regulation), focusing on cybercrime penalties and network security.
Department of Telecommunications
The central government body under the Ministry of Communications responsible for formulating telecom policies, licensing, and enforcing regulations like the prevention of IMEI tampering.
UPSC context
Relevant for GS Paper II (Government Policies & Intervention) and GS Paper III (Internal Security and Cyber threats).
সংযুক্ত স্থির ধারণা
What is the Central Equipment Identity Register (CEIR) and how does it function in India?
- Nodal Agency: Nodal Agency,Managed by the Department of Telecommunications (DoT) to curb mobile theft and counterfeiting.
- Cross-Network Blocking: Cross-Network Blocking,Shares IMEI database across all telecom operators to block stolen or lost mobile phones nationwide.
- Consumer Portal: Consumer Portal,Integrates with the 'Know Your Mobile' (KYM) service for verifying device authenticity before purchase.
আন্তঃবিষয় প্যাটার্ন
Cyber Security + Internal Security Challenges
Internal security threats via cloned devices intersect directly with telecommunications interception laws and national identity databases (Aadhaar/SIM linking).

CEIR, KYM portal, and IMEI tampering offenses under the Telecommunications Act 2023 make a high-yield prelims match.
সংযুক্ত PYQ · 3
সংযুক্ত PYQ · 3
- 2020MainsGS3
Discuss different types of cyber crimes and measures required to be taken to fight the menace.
- 2021MainsGS3
Keeping in view India's internal security, analyse the impact of cross-border cyber attacks. Also discuss defensive measures against these sophisticated attacks.
- 2025MainsGS2
e-governance projects have a built-in bias towards technology and back-end integration than user-centric designs. Examine.
