दूरसंचार विनियमन और बौद्धिक संपदा अधिकार
स्रोत:द हिंदू ↗
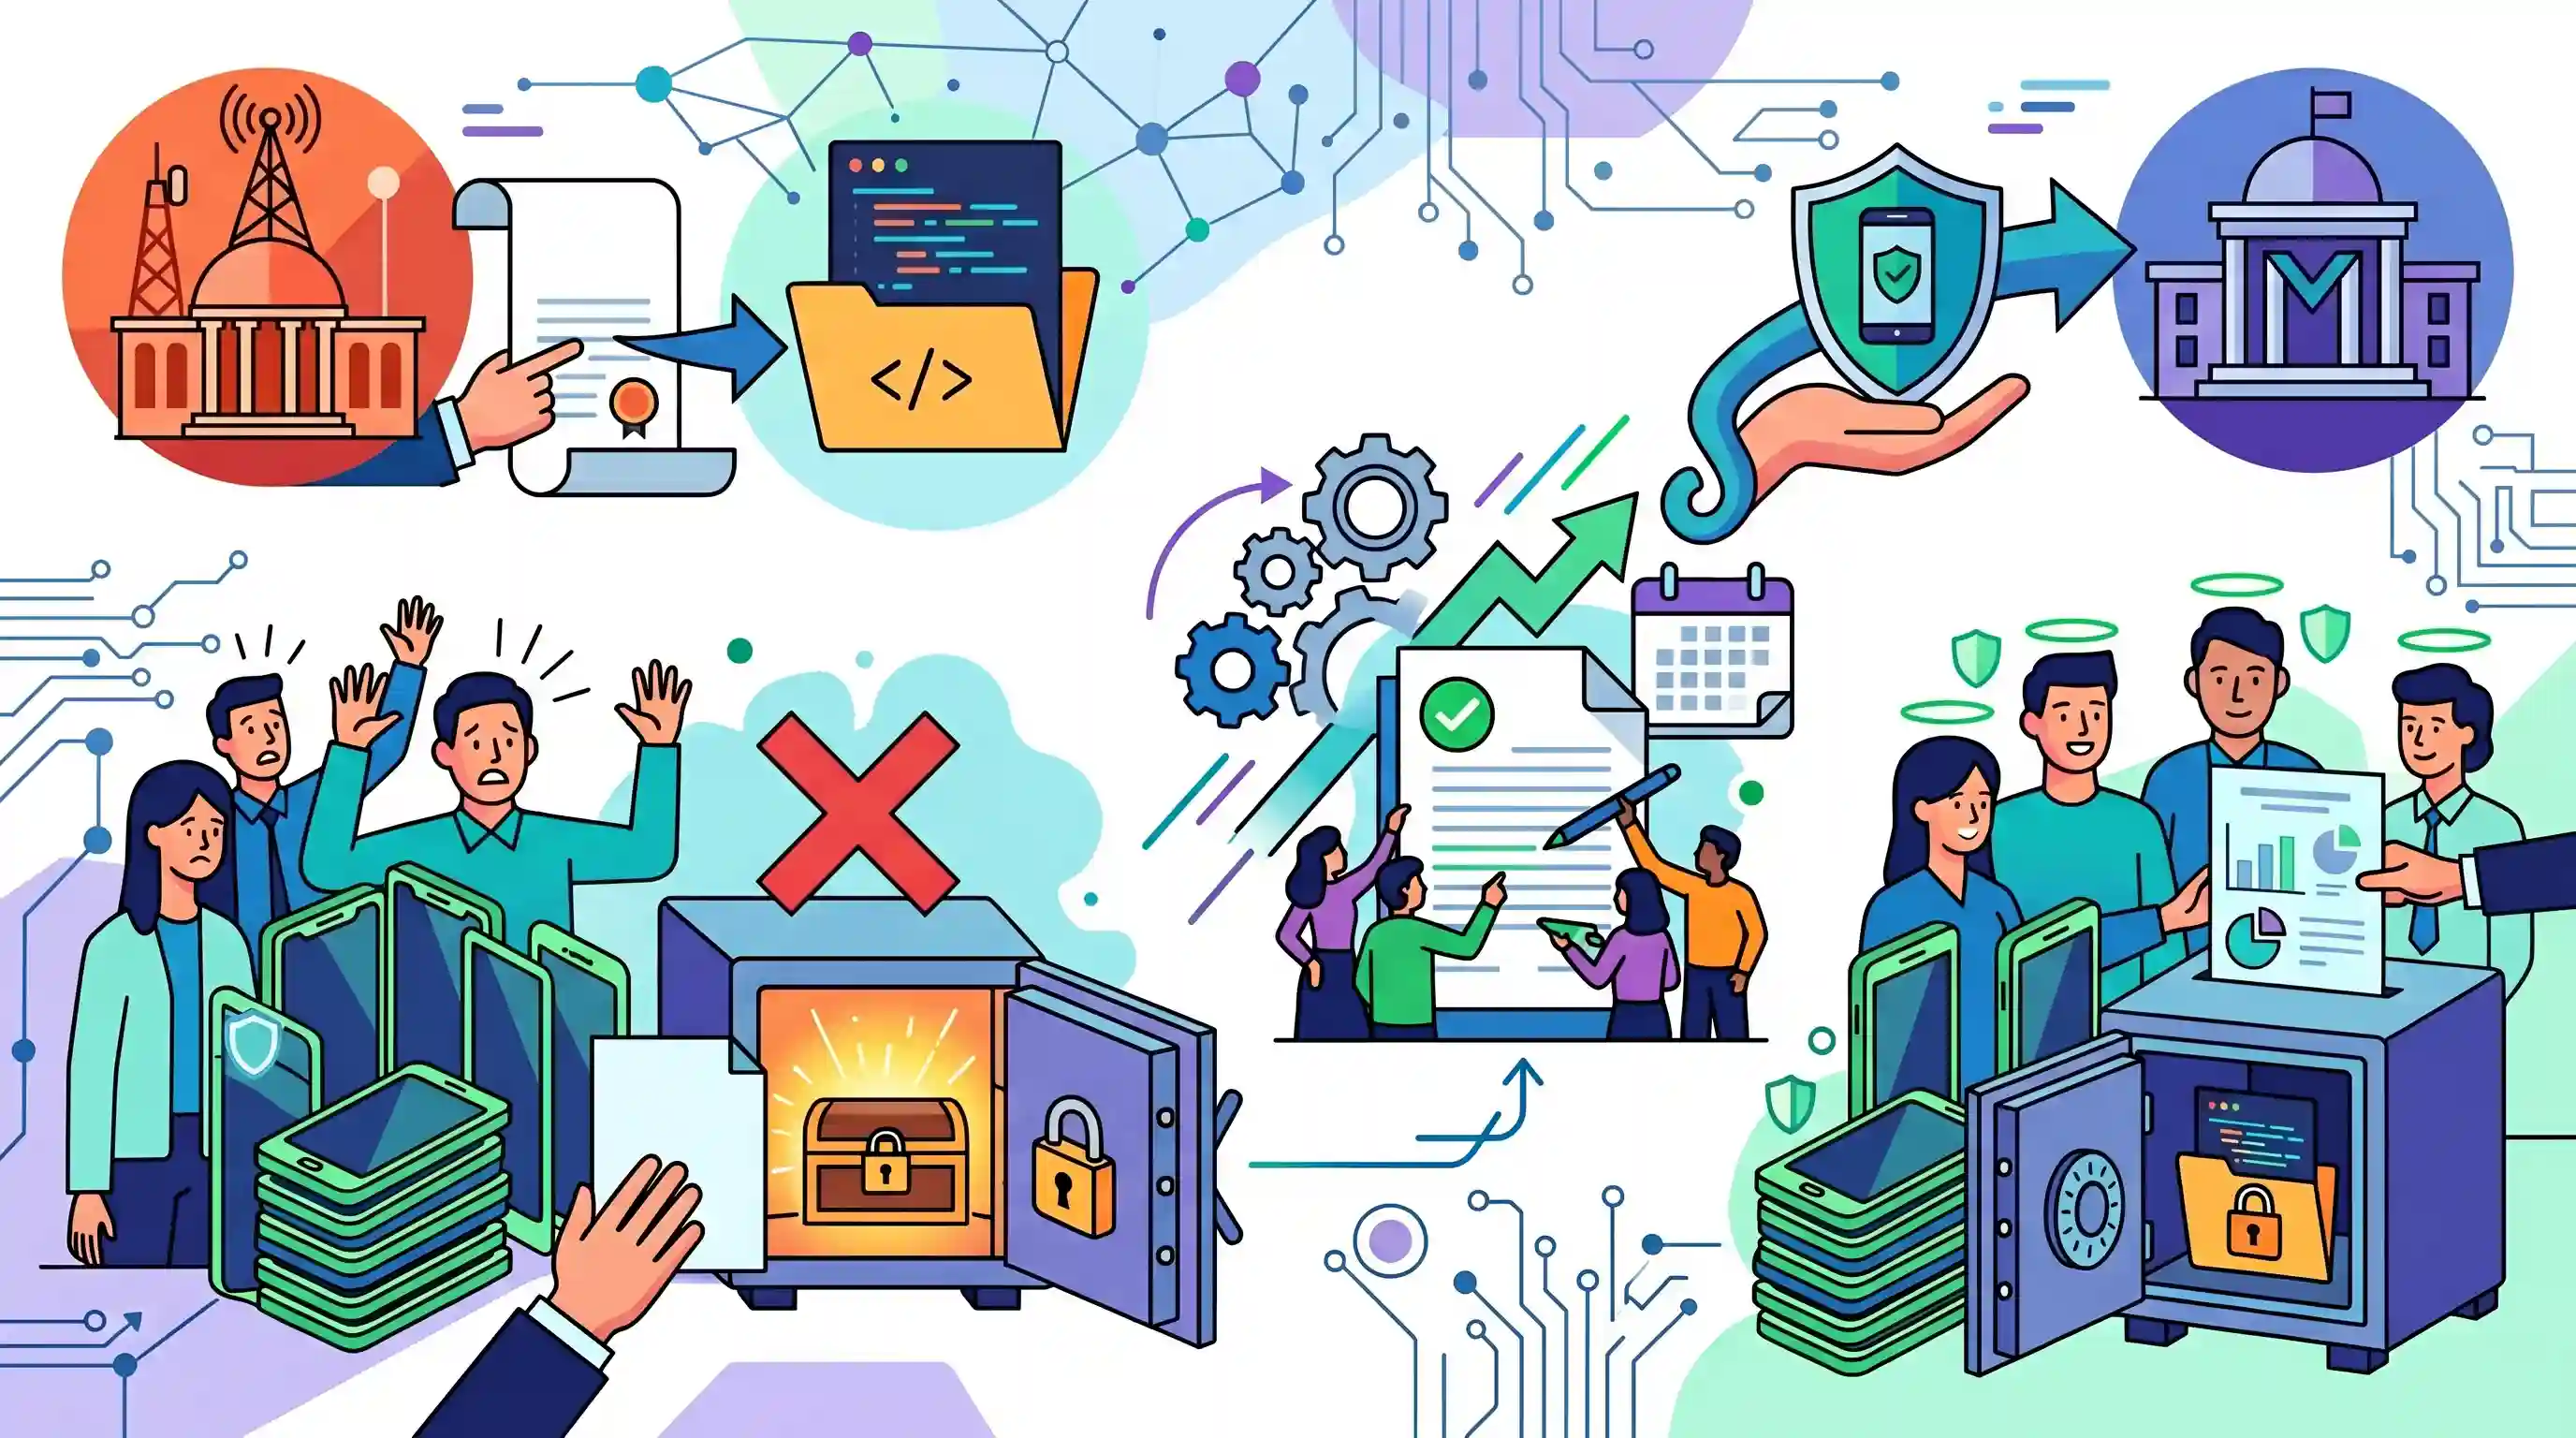
क्यों मायने रखता है
Highlights the ongoing regulatory balancing act between ensuring robust national cybersecurity (vetting hardware and software for backdoors) and protecting corporate intellectual property (IPR) rights like trade secrets. It is highly relevant for GS-3 topics involving internal security challenges in cyberspace, telecommunications infrastructure, and intellectual property.
सारांश
The Ministry of Electronics and Information Technology (MeitY) and the smartphone industry body MAIT have denied reports that the government mandated manufacturers to share their operating system source codes. The alarm was triggered by a 2023 draft of the Indian Telecom Security Assurance Requirement (ITSAR) created by the DoT’s National Centre for Communication Security, which sought source code disclosure for security vulnerability tests. After the industry expressed significant concerns regarding intellectual property (IPR) violations, the government amended the guidelines in June 2025. The new rules only require an internal test report outlining vulnerabilities without compromising proprietary IP information. Furthermore, jurisdiction over smartphone security has been shifted from DoT to MeitY.
मुख्य बिंदु
- The IT Ministry (MeitY) and the Manufacturers’ Association for Information Technology (MAIT) have clarified that the government has not demanded source codes of smartphone operating systems.
- Confusion originally stemmed from a 2023 draft of the Indian Telecom Security Assurance Requirement (ITSAR) issued by the Department of Telecommunications (DoT), which included a clause mandating source code disclosure for vulnerability analysis.
- Following industry pushback citing concerns over intellectual property (IP) rights, the clause was amended in June 2025 to remove the source code requirement.
- संशोधित दिशा-निर्देशों के तहत, निर्माताओं को एक आंतरिक परीक्षण रिपोर्ट प्रस्तुत करनी होगी जिसमें भेद्यता आकलन (vulnerability assessments) का विवरण हो, जिसमें स्पष्ट रूप से प्रोपराइटरी IP जानकारी को बाहर रखा गया हो।
- स्मार्टफोन हार्डवेयर और ऑपरेटिंग सिस्टम सुरक्षा के लिए नियामक देखरेख (Regulatory oversight) को अब DoT से MeitY को स्थानांतरित कर दिया गया है।
महत्वपूर्ण शब्द
भारतीय दूरसंचार सुरक्षा आश्वासन आवश्यकता (ITSAR)

दूरसंचार उपकरणों के परीक्षण और प्रमाणन के लिए DoT के तहत NCCS द्वारा विकसित सुरक्षा मानक। ये साइबर खतरों और अनधिकृत कमजोरियों के खिलाफ बुनियादी ढांचे के लचीलेपन (resilience) को सुनिश्चित करते हैं।
UPSC context
GS Paper III: साइबर सुरक्षा। यह महत्वपूर्ण संचार बुनियादी ढांचे की अखंडता सुनिश्चित करने वाले विनियामक ढांचों की समझ का परीक्षण करता है।
National Centre for Communication Security (NCCS)
दूरसंचार विभाग के तहत एक विशेष केंद्र जो राष्ट्रीय सुरक्षा की रक्षा के लिए सुरक्षा मानक (ITSAR) विकसित करने और टेलीकॉम उत्पादों को प्रमाणित करने के लिए जिम्मेदार है।
UPSC context
GS Paper III: Security. Relevant for institutional measures against data breaches and supply chain vulnerabilities in telecom.
Ministry of Electronics and Information Technology (MeitY)
The nodal ministry for electronics, IT, and digital governance policy. It spearheads Digital India and regulates cybersecurity through agencies like CERT-In.
UPSC context
GS पेपर II: सरकारी नीतियां। तकनीकी संप्रभुता और डिजिटल विनियमन को संचालित करने वाली नोडल एजेंसियों के ज्ञान का परीक्षण करता है।
Manufacturers’ Association for Information Technology (MAIT)
The apex industry body representing India’s IT hardware and electronics sector. It advocates for policy reforms, domestic manufacturing, and IPR protection.
UPSC context
GS Paper II: Pressure Groups/Associations. Exemplifies how industry bodies influence government policy and balance security with business interests.
Department of Telecommunications (DoT)
संचार मंत्रालय के अधीन एक विभाग जो दूरसंचार लाइसेंसिंग, स्पेक्ट्रम प्रबंधन और दूरसंचार में अंतर्राष्ट्रीय समन्वय के लिए उत्तरदायी है।
UPSC context
GS Paper II: Statutory/Regulatory Bodies. Tests understanding of inter-departmental jurisdiction and regulatory shifts in the tech sector.
प्रारंभिक ट्रैप
ITSAR दिशानिर्देशों के तहत, स्मार्टफोन निर्माताओं को सुरक्षा मंजूरी के लिए अपने OS सोर्स कोड को DoT के साथ साझा करना अनिवार्य होगा।
The source code mandate was dropped in June 2025 to protect IPR. Furthermore, smartphone security jurisdiction has shifted from DoT to MeitY.
संबंधित अवधारणाएँ
भारत में प्रोप्रायटरी सॉफ्टवेयर और सोर्स कोड को कैसे संरक्षित किया जाता है?
- Copyright Law: कंप्यूटर प्रोग्राम, उनके सोर्स कोड सहित, कॉपीराइट अधिनियम, 1957 के तहत "साहित्यिक कार्यों" के रूप में संरक्षित हैं।
- व्यापारिक रहस्य: भारत में ट्रेड सीक्रेट के लिए कोई समर्पित कानून (statute) नहीं है; इसका संरक्षण भारतीय अनुबंध अधिनियम (Indian Contract Act) और गोपनीयता के उल्लंघन को नियंत्रित करने वाले कॉमन लॉ सिद्धांतों पर निर्भर करता है।
साइबर सुरक्षा अधिकार क्षेत्र DoT और MeitY के बीच कैसे विभाजित है?
- DoT (Telecom): Secures core telecom networks and equipment. NCCS formulates the Indian Telecom Security Assurance Requirements (ITSAR) for network infrastructure.
- MeitY (IT): व्यापक साइबर सुरक्षा (CERT-In), डेटा सुरक्षा, इलेक्ट्रॉनिक्स विनिर्माण, और स्मार्टफोन हार्डवेयर तथा ऑपरेटिंग सिस्टम सुरक्षा की निगरानी को विनियमित करता है।
अंतर-विषय पैटर्न
टेलीकॉम सप्लाई चेन सुरक्षा
ITSAR की आवश्यकताएं सीधे तौर पर दूरसंचार क्षेत्र पर राष्ट्रीय सुरक्षा निर्देश (NSDTS) से जुड़ी हैं, जो साइबर बैकडोर (cyber backdoors) को रोकने के लिए टेलीकॉम कंपनियों द्वारा विशेष रूप से निर्दिष्ट 'Trusted Sources' से ही खरीद को अनिवार्य बनाता है।
Algorithmic Transparency vs. IPR
The pushback against sharing source code mirrors global AI regulation debates, where states want to audit algorithms for security vulnerabilities while tech companies refuse to expose core intellectual property.

Expect a 2026 prelims statement testing the exact regulatory boundary between DoT (telecom networks) and MeitY (smartphone OS security).
संबद्ध PYQ · 2
संबद्ध PYQ · 2
- 2017MainsGS3
Discuss the potential threats of Cyber attack and the security framework to prevent it.
- 2014MainsGS3
In a globalized world, Intellectual Property Rights assume significance and are a source of litigation. Broadly distinguish between the terms-Copyrights, Patents and Trade Secrets.
