Cybersecurity and Protection of India Critical Infrastructure
Source:The Hindu ↗
Why It Matters
The protection of Critical Information Infrastructure is a core component of India's internal security matrix. UPSC consistently tests candidates on India's cybersecurity framework, the role of agencies like NCIIPC and CERT-In, and defensive measures against cross-border state-sponsored cyber warfare.
Summary
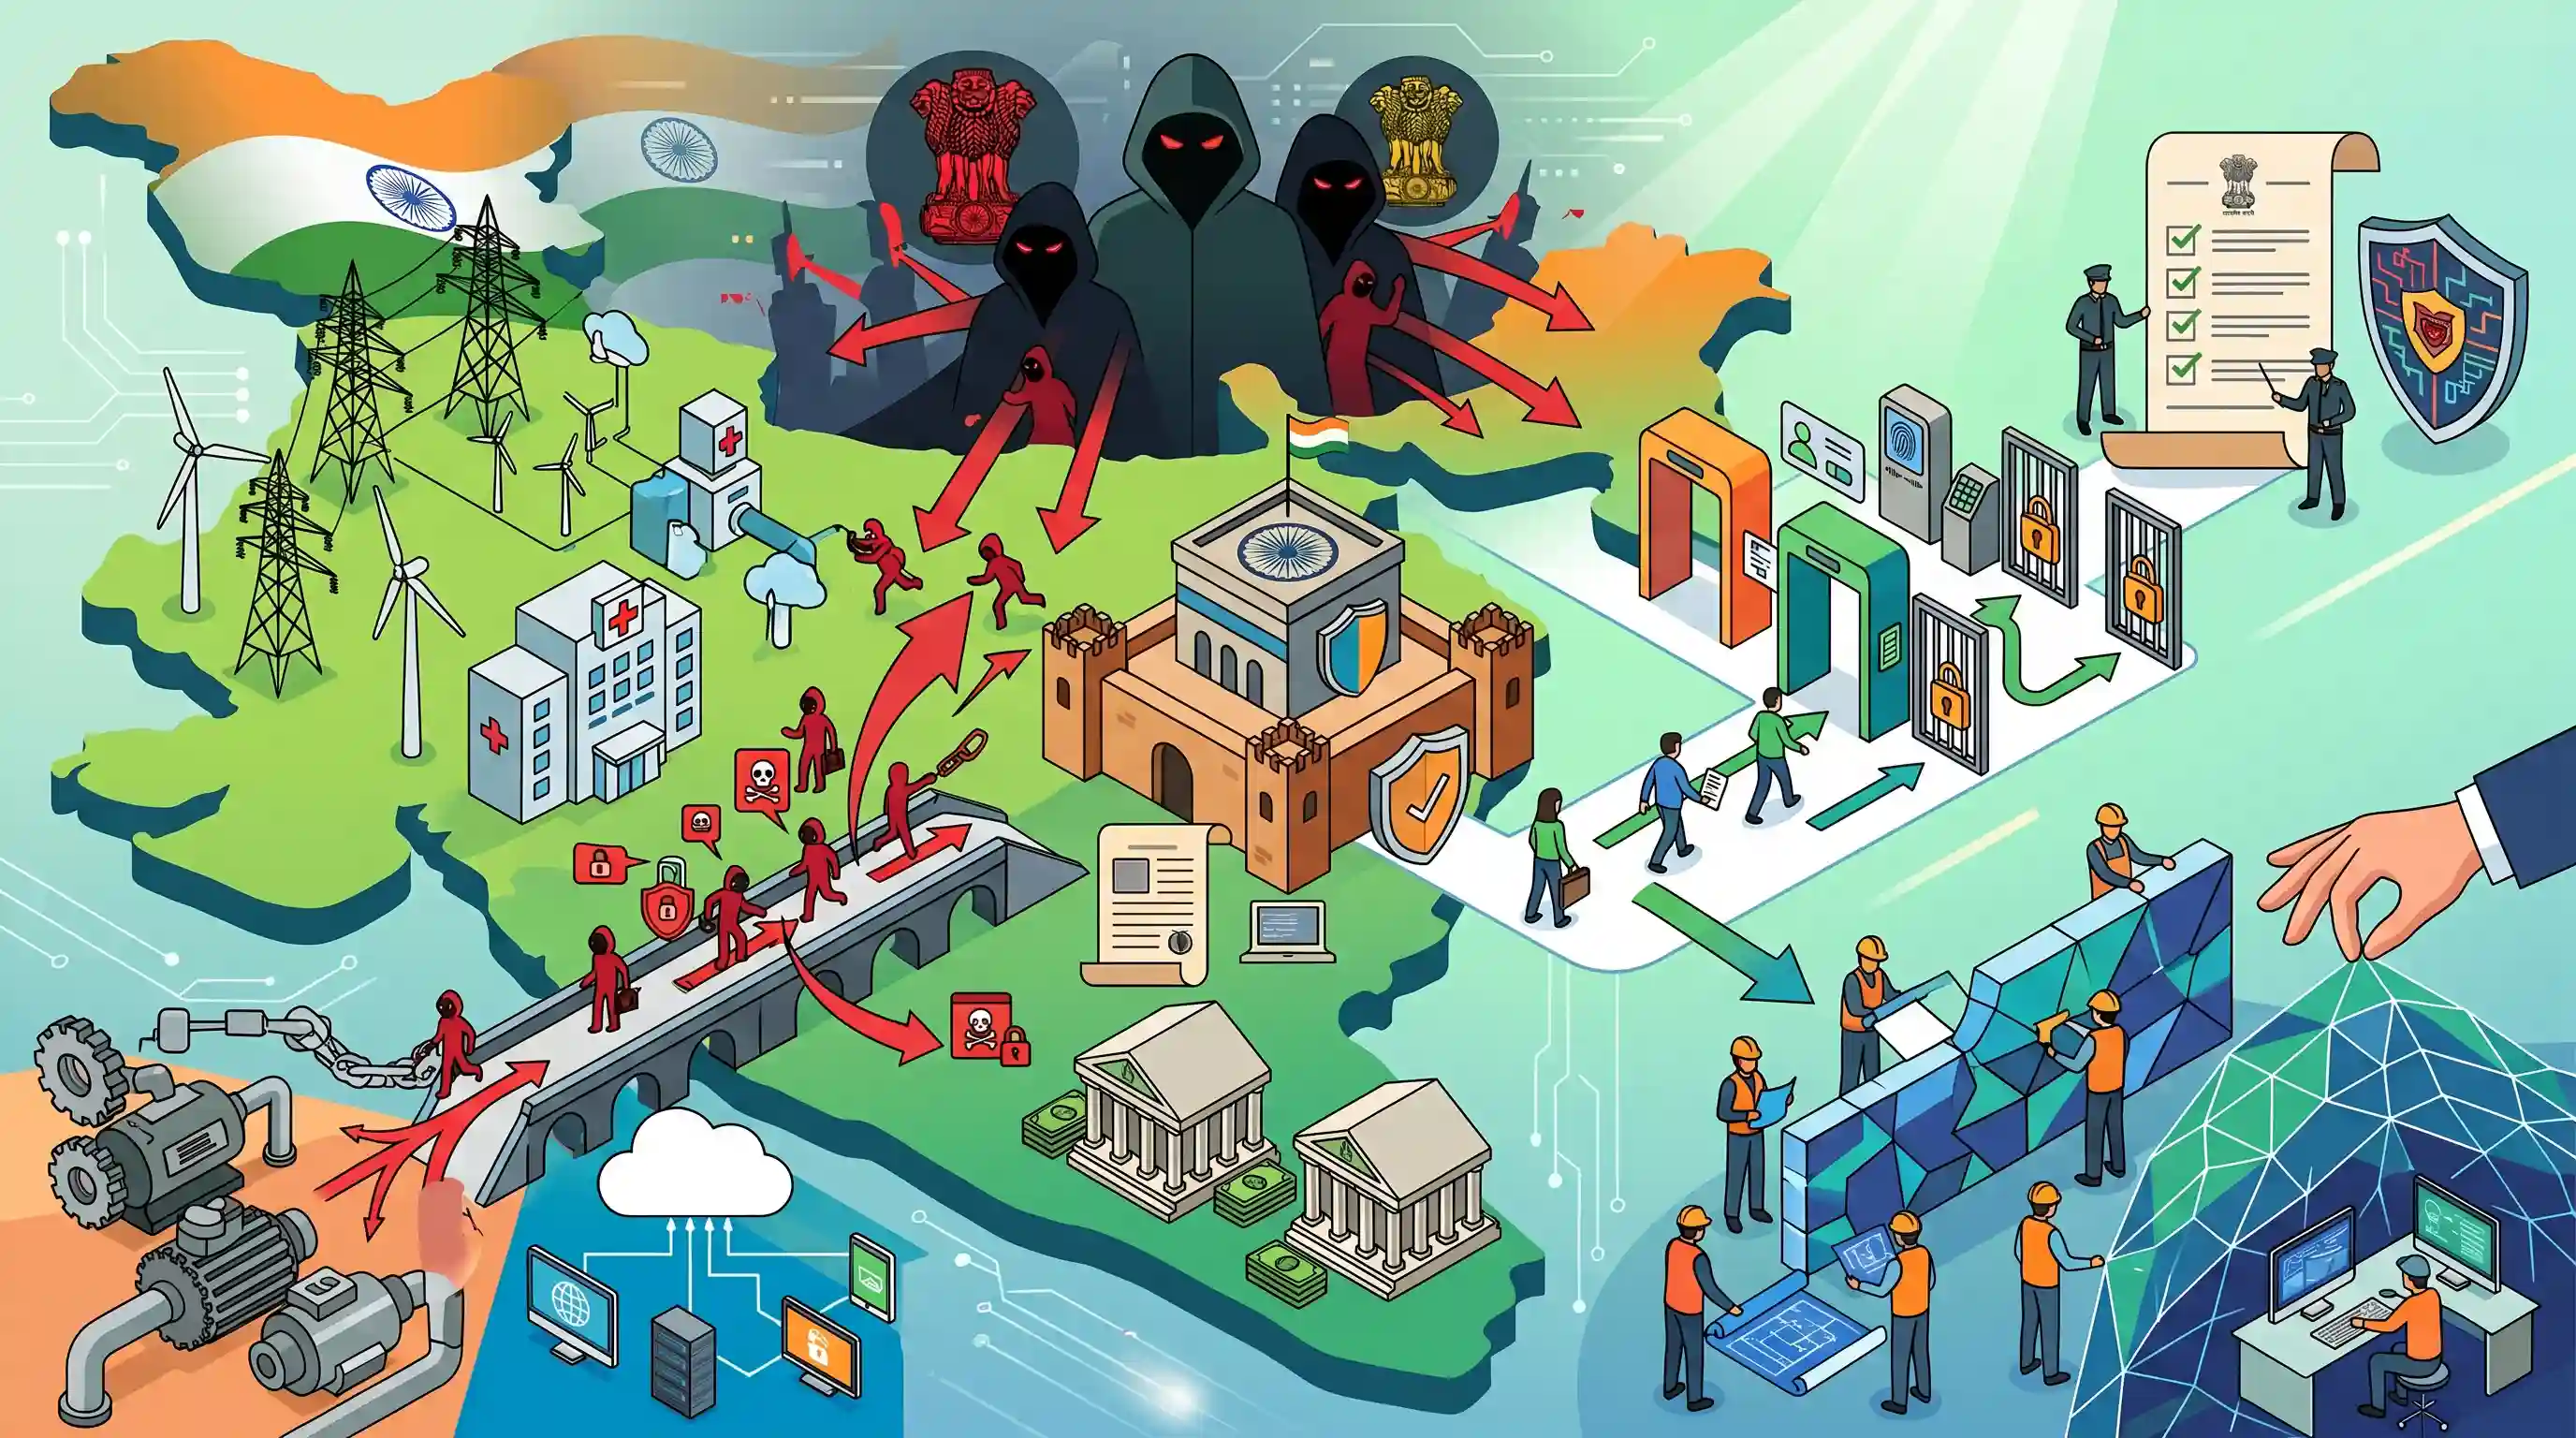
The article evaluates the cybersecurity posture of India’s Critical National Infrastructure (CNI), such as power grids, healthcare, and financial systems. It highlights how the convergence of legacy Operational Technology (OT) with internet-facing Information Technology (IT) networks has widened the attack surface, as evidenced by recent high-profile cyber intrusions and ransomware attacks. While the Information Technology Act, 2000 established the National Critical Information Infrastructure Protection Centre (NCIIPC) to safeguard these assets, the persistent nature of state-sponsored Advanced Persistent Threats (APTs) demands a more robust defense mechanism. The piece advocates for implementing zero-trust architecture, strict adherence to CERT-In guidelines, and the rapid deployment of an updated National Cyber Security Strategy to ensure the resilience of India's strategic digital assets.
Key Points
- Critical Information Infrastructure (CII) is defined under Section 70 of the IT Act, 2000, covering sectors whose incapacitation would have a debilitating impact on national security, economy, or public health.
- The NCIIPC is the nodal agency designated to protect India's CII, functioning alongside CERT-In which handles broader incident response.
- The convergence of Information Technology (IT) and Operational Technology (OT) in sectors like power and healthcare has introduced severe vulnerabilities, exposing legacy systems to modern cyber threats.
- Recent incidents, including ransomware attacks on hospitals (like AIIMS) and suspected state-sponsored intrusions into power grids, highlight the persistent threat of Advanced Persistent Threats (APTs).
- Strengthening CII requires mandatory incident reporting, adoption of zero-trust architecture, air-gapping critical OT networks, and continuous capacity building for cyber defense.
Important Terms
Information Technology Act, 2000

The primary legislation in India governing cybercrime and electronic commerce, providing legal recognition to digital signatures and defining offenses like hacking and data theft.
UPSC context
GS Paper 3: Internal Security and Science & Technology; central to legal framework for cyber security and digital governance.
National Critical Information Infrastructure Protection Centre (NCIIPC)
A specialized unit of NTRO established under Section 70A of the IT Act to protect critical sectors like power, banking, and telecom from cyber threats.
UPSC context
GS Paper 3: Internal Security; tests knowledge of nodal agencies for Critical Information Infrastructure (CII) protection.
CERT-In (Computer Emergency Response Team - India)
The national nodal agency for responding to cybersecurity incidents, forecasting threats, and issuing emergency guidelines, established under Section 70B of the IT Act.
UPSC context
GS Paper 3: Internal Security; essential for understanding India's reactive and proactive cybersecurity posture.
National Technical Research Organisation (NTRO)
A technical intelligence agency under the National Security Advisor (PMO) responsible for satellite monitoring, cyber intelligence, and overseeing the NCIIPC.
UPSC context
GS Paper 3: Security Forces and Agencies; tests awareness of technical intelligence and oversight of critical digital assets.
National Cyber Security Strategy
A comprehensive framework conceptualized in 2020 to enhance India's cyber resilience, improve institutional synergy, and secure large-scale digitization of public services.
UPSC context
GS Paper 3: Internal Security; crucial for discussing policy evolution and future roadmap for India's digital defense.
National Cyber Security Policy 2013
The first comprehensive framework aimed at building a secure and resilient cyberspace for citizens and businesses while protecting sovereign data.
UPSC context
GS Paper 3: Internal Security; historical baseline for cybersecurity policy analysis in India.
Prelims Trap
"CERT-In is the designated nodal agency for protecting India's Critical Information Infrastructure."
NCIIPC is the specific nodal agency for CII protection (Sec 70A of IT Act), while CERT-In handles broader national cyber incident response (Sec 70B).
Static Concepts Connected
What are the differing statutory mandates of NCIIPC and CERT-In?
- NCIIPC (CII): Designated under Sec 70A of the IT Act specifically to protect Critical Information Infrastructure (CII); functions under NTRO.
- CERT-In (Response): Established under Sec 70B of the IT Act as the national nodal agency for overarching cyber incident response and threat forecasting (under MeitY).
How do IT (Information Technology) and OT (Operational Technology) differ?
- IT (Data-focused): Manages enterprise data flow and processing (e.g., servers, databases). Focuses primarily on confidentiality, integrity, and availability of digital information.
- OT (Physical-focused): Monitors and controls physical devices, processes, and events (e.g., SCADA systems in power grids). Prioritizes physical safety and continuous system operation.
Cross-Topic Patterns
Cyber-warfare & State Actors
State-sponsored Advanced Persistent Threats (APTs) targeting physical infrastructure (like power grids) blend traditional GS-3 Internal Security with GS-2 Geopolitics and bilateral gray-zone warfare.
Cyber-resilience in Disaster Management
Debilitating attacks on healthcare (AIIMS) or power sectors elevate cyber-intrusions from IT issues to national disasters, linking cyber strategy with the Disaster Management Act framework.

Expect a 2026 multi-statement Prelims question contrasting the exact statutory mandates of NCIIPC, CERT-In, and NTRO under the IT Act.
Linked PYQs · 5
Linked PYQs · 5
- 2022MainsGS3
What are the different elements of cyber security ? Keeping in view the challenges in cyber security, examine the extent to which India has successfully developed a comprehensive National Cyber Security Strategy.
- 2021MainsGS3
Keeping in view India's internal security, analyse the impact of cross-border cyber attacks. Also discuss defensive measures against these sophisticated attacks.
- 2017MainsGS3
Discuss the potential threats of Cyber attack and the security framework to prevent it.
- 2020PrelimsGS1
In India, the term "Public Key Infrastructure" is used in the context of
- 2020PrelimsGS1
In India, under cyber insurance for individuals, which of the following benefits are generally covered, in addition to payment for the loss of funds and other benefits? 1. Cost of restoration of the computer system in case of malware disrupting access to one's computer 2. Cost of a new computer if some miscreant wilfully damages it, if proved so 3. Cost of hiring a specialized consultant to minimize the loss in case of cyber extortion 4. Cost of defence in the Court of Law if any third party files a suit Select the correct answer using the code given below:
